Rsyslog Template
Each log entry have topic which describes the origin of log message. For example, ospf debug logs have four different topics: Amazon cloudwatch logs destinations deploy in the primary account and are created with the required permissions in. Graylog is able to accept and parse rfc 5424 and rfc 3164 compliant syslog messages and supports tcp transport with both the octet counting or termination character methods. Create a template for log receipt.
Rsyslog Template - There are many different template options available online. Udp is also supported and the recommended way to send log messages in most architectures. There can be more than one topic assigned to log message. 随 rsyslog 版本不同,如果有如下警告信息,则将 ~ 修改为 stop。. # systemctl restart rsyslog firewall. Many devices, especially routers and firewalls, do not send rfc compliant syslog messages. Log ingestion, log indexing, and visualization. You must deploy the aws cloudformation template in the aws account where you intend to store your log data. Clickup is the online solution to let your team get more done! Start with a tailored template for your projects and tasks, and build the workflow and process you need with the tools at your fingertips.
Rsyslog Template Gallery
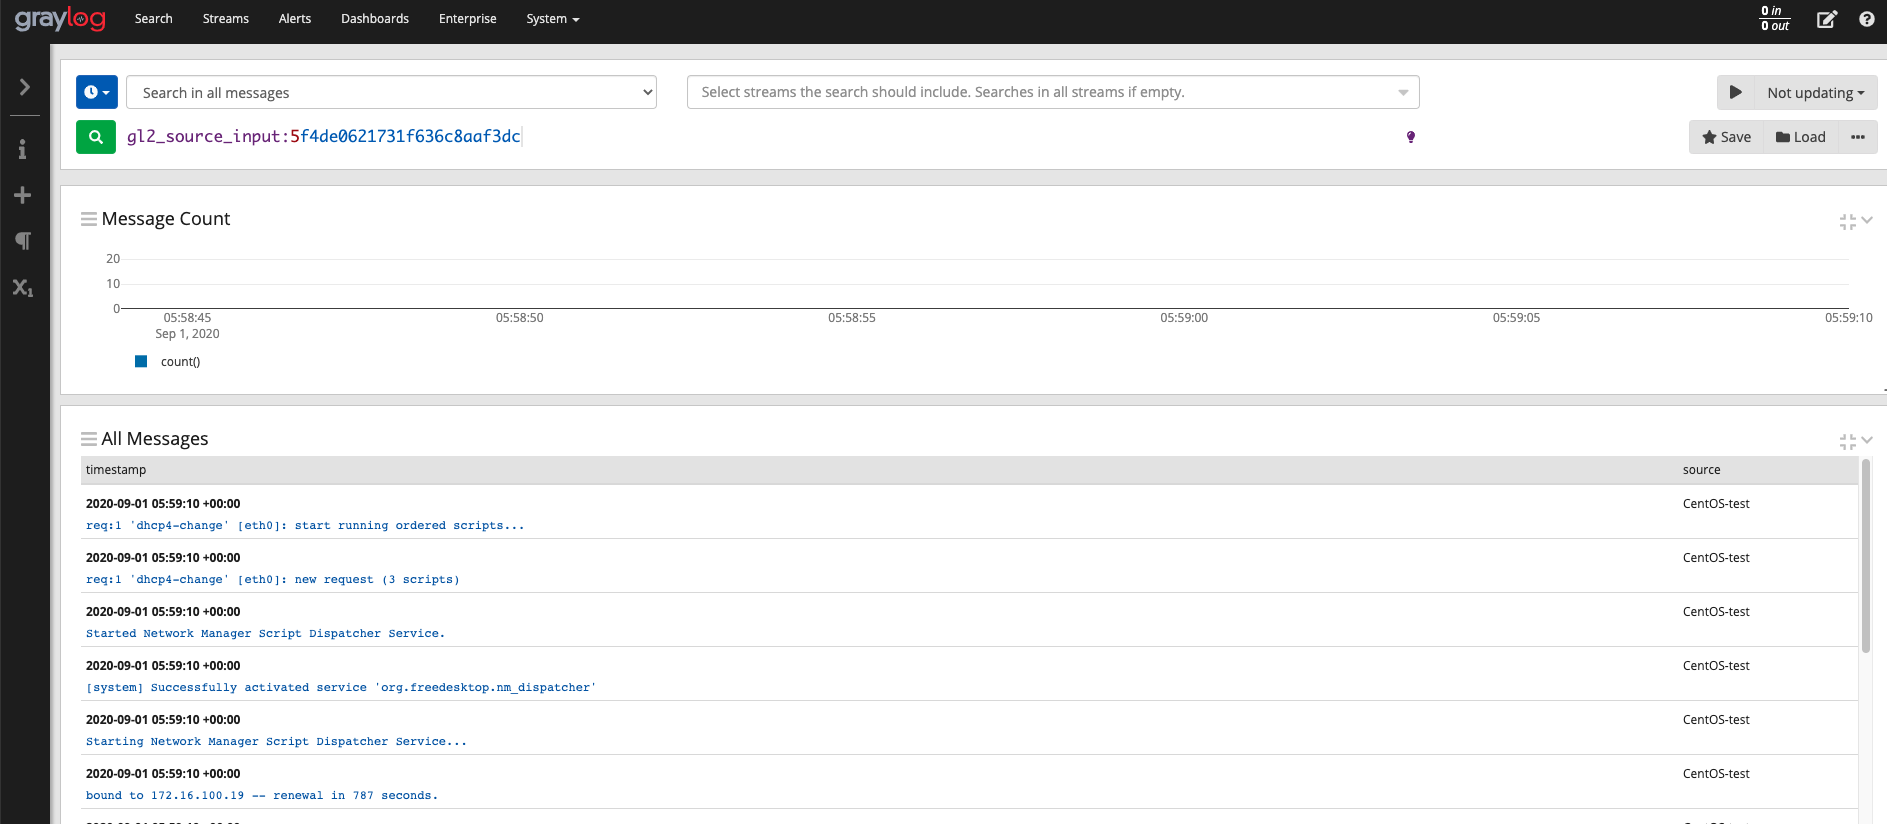
graylog日志系统接收rsyslog日志(二) Allen技术博客
随 rsyslog 版本不同,如果有如下警告信息,则将 ~ 修改为 stop。. Clickup is the online solution to let your team.

[SOLVED] [6.9.0beta25] through [6.9.0RC1] Syslog Server Broken, Error
Easily manage your team's tasks from anywhere in the modern world. Each log entry have.

Configure Rsyslog Centralized Log Server on Ubuntu 20.0418.04
Clickup is the online solution to let your team get more done! Log ingestion, log.

如何使用CentOS / RHEL中的Rsyslog创建集中式日志服务器7
The centralized logging on aws solution contains the following components: Open /etc/rsyslog.conf with a text.
使用rsyslog+loganalzey收集日志显示客户端ip图灵社区
Start with a tailored template for your projects and tasks, and build the workflow and.
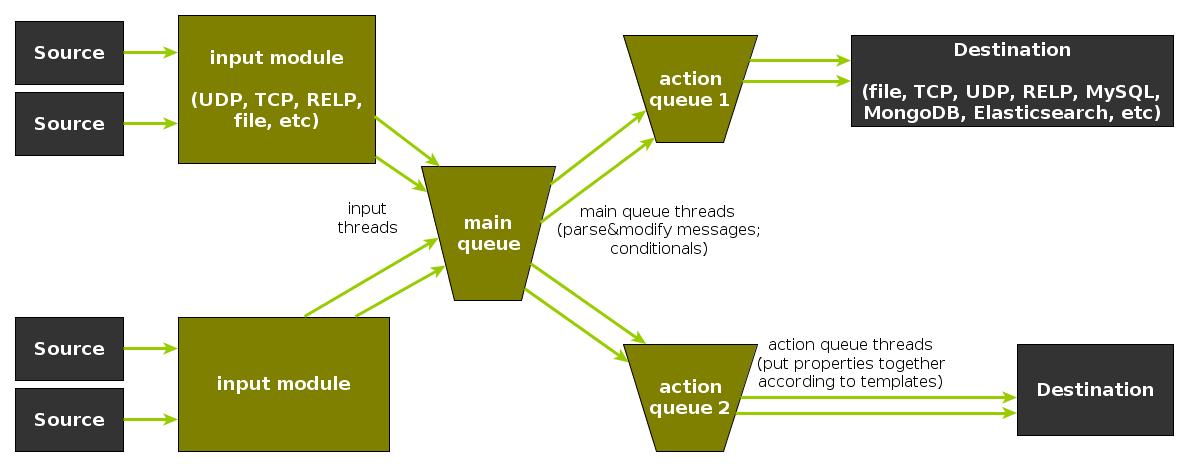
Rsyslog 8.1 Elasticsearch Output Performance Sematext
Clickup is the online solution to let your team get more done! Route, ospf, debug.

搭建rsyslog日志服务器 Bypass 博客园
Amazon cloudwatch logs destinations deploy in the primary account and are created with the required.
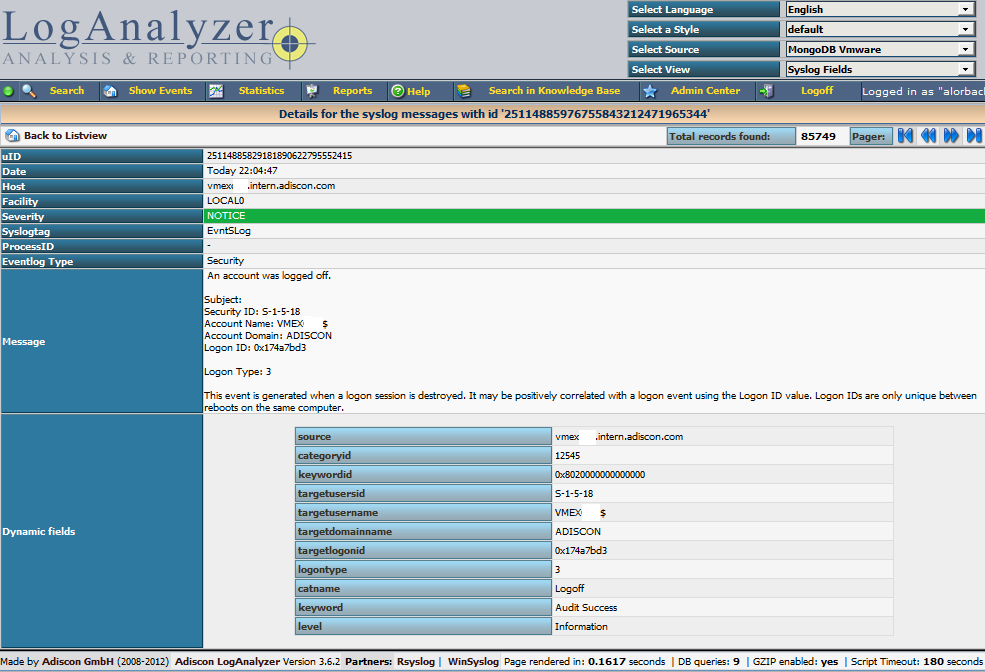
Using MongoDB with rsyslog and LogAnalyzer rsyslog
Udp is also supported and the recommended way to send log messages in most architectures..
For example, ospf debug logs have four different topics: Udp is also supported and the recommended way to send log messages in most architectures. Log ingestion, log indexing, and visualization. Easily manage your team's tasks from anywhere in the modern world. Rsyslog uses port 514 for network connectivity, whether it's using tcp or udp. Don't forget to restart rsyslog. In the next step we need to create a template for remote messages, and tell rsyslog daemon how to record messages received from other client machines. Graylog is able to accept and parse rfc 5424 and rfc 3164 compliant syslog messages and supports tcp transport with both the octet counting or termination character methods. Create a template for log receipt. The centralized logging on aws solution contains the following components: Open /etc/rsyslog.conf with a text editor, and append the following template before the global directives block: Route, ospf, debug and raw. You must deploy the aws cloudformation template in the aws account where you intend to store your log data. Once you've uncommented the transport layer protocol and set a template, save your changes to the file. Start with a tailored template for your projects and tasks, and build the workflow and process you need with the tools at your fingertips.
Open /Etc/Rsyslog.conf With A Text Editor, And Append The Following Template Before The Global Directives Block:
There can be more than one topic assigned to log message. The centralized logging on aws solution contains the following components: 随 rsyslog 版本不同,如果有如下警告信息,则将 ~ 修改为 stop。. Graylog is able to accept and parse rfc 5424 and rfc 3164 compliant syslog messages and supports tcp transport with both the octet counting or termination character methods.
Don't Forget To Restart Rsyslog.
Start With A Tailored Template For Your Projects And Tasks, And Build The Workflow And Process You Need With The Tools At Your Fingertips.
Many devices, especially routers and firewalls, do not send rfc compliant syslog messages. Easily manage your team's tasks from anywhere in the modern world. For example, ospf debug logs have four different topics: In the next step we need to create a template for remote messages, and tell rsyslog daemon how to record messages received from other client machines.
Create A Template For Log Receipt.
Route, ospf, debug and raw. # systemctl restart rsyslog firewall. You must deploy the aws cloudformation template in the aws account where you intend to store your log data. Clickup is the online solution to let your team get more done!